



Critical event management platforms help organizations identify, communicate, and respond to critical events that threaten people, operations, facilities, IT systems, or business continuity. Modern critical event management software can combine event management, mass notification, situational awareness, incident response, and operational resilience – but not every platform approaches critical event management in the same way.
Some CEM platforms focus on risk intelligence and threat monitoring. Others specialize in mass notification and emergency communications. And increasingly, organizations need strong operational response capabilities that make sure the right people are alerted, acknowledge an incident, and take action.
Understanding these differences is key to choosing the right critical event management solution for your organization.
What Is a Critical Event Management Platform?
Critical event management, or CEM, combines the technology and processes organizations use to identify, assess, communicate, and respond to disruptive events.
These events can range from natural disasters and severe weather to cyberattacks, IT outages, industrial incidents, workplace safety threats, and supply chain disruptions.
Depending on its focus, a CEM platform may include:
- Risk intelligence and threat monitoring
- Situational awareness
- Mass notification and emergency communications
- Crisis communication
- Incident management and incident response
- On-call alerting and escalation
- Response plans and automated workflows
- Analytics and incident analysis
The goal is not simply to know that something has happened. Effective critical event management helps organizations understand what is happening, reach the right people, coordinate their response, and restore normal operations.
That makes CEM an important part of both business continuity and operational resilience.
What Counts as a Critical Event?
A critical event is any disruptive event with the potential to significantly affect people, assets, infrastructure, services, or business operations.
What qualifies as critical depends on the organization.
A hospital may need to respond to a power failure affecting critical equipment. A manufacturer may face an industrial safety incident or production line failure. An IT organization might be dealing with a major service outage or cyberattack. Governments and public-sector organizations may need to manage natural disasters, severe weather events, infrastructure failures, or public safety emergencies.
Other examples include supply chain disruptions, workplace emergencies, facility outages, equipment failures, and IoT or operational technology events.
The common denominator is impact: the event requires awareness, communication, and coordinated action.
How Does Critical Event Management Work?
While crises can look very different, the underlying CEM process often follows a similar path:

Detect and Assess
The first step is identifying a potential threat or disruption.
Depending on the organization, this may involve real-time threat intelligence, weather feeds, security tools, IT monitoring systems, IoT sensors, industrial control systems, or other data sources.
Situational awareness then provides context. What happened? Who or what is affected? How serious is the potential impact? Does the event require immediate action?
Not every CEM platform provides its own threat monitoring. Many integrate with specialized systems that already detect these events.
Communicate and Alert
Once a critical event has been identified, relevant people need to know.
Mass notification systems can distribute emergency notifications to large groups via SMS, voice calls, email, mobile push notifications, and other channels. This is particularly important for employee safety, emergency management, and crisis communication.
But informing people and mobilizing responders are not always the same thing.
Operational incidents may require targeted alerting: Who is on call? Which engineer, security analyst, technician, or response team needs to act? What happens if that person is unavailable?
Respond, Escalate, and Resolve
This is where communication becomes action.
A critical event management process should provide visibility into whether someone has received and acknowledged an alert and taken ownership of the incident.
If nobody responds within the required time, automated escalation can alert additional responders according to predefined response plans.
During the response itself, incident management and collaboration tools help teams coordinate actions and track remediation processes through resolution.
Analyze and Improve
After an incident, analytics and incident analysis can reveal how effectively the organization responded.
How quickly was the event detected? How long did it take to alert responders? When was the incident acknowledged? How quickly did remediation begin? Where did delays occur?
These insights help organizations improve response plans and strengthen operational resilience over time.
CEM vs. Mass Notification vs. Incident Management
Several technology categories address different parts of critical event management, and the terminology can become confusing.
Mass notification systems focus primarily on reaching large groups of people quickly. During a crisis, they might send emergency communications to hundreds or thousands of employees, customers, or other stakeholders.
Risk intelligence and threat monitoring focus on identifying potential threats and providing real-time information about events such as severe weather, natural disasters, security threats, or other external risks.
Incident management focuses on organizing and tracking the process of resolving incidents. In IT, for example, incident management software may create tickets, assign incidents, document actions, and track progress.
On-call alerting and response focus on getting critical information to the specific people who need to act. This includes duty scheduling, targeted alerts, acknowledgments, automated escalation, and tracking who has taken ownership.
Critical event management takes a broader view, connecting some or all of these capabilities into a coordinated process.
Modern CEM platforms may provide many of these functions themselves or integrate specialized software to create a broader critical event management ecosystem.
Core Capabilities of Modern CEM Platforms
There is no single feature set that defines every CEM platform. However, several capabilities are important when evaluating critical event management software.
Risk Intelligence and Situational Awareness
Organizations need timely information about potential threats and enough context to determine whether action is required.
Depending on the use case, this may include real-time risk intelligence about natural disasters and severe weather events or events from cybersecurity, IT monitoring, IoT, building management, and industrial systems.
Mass Notification and Emergency Communications
Reliable communication is central to crisis management.
Multi-channel mass notification can help organizations quickly distribute warnings, instructions, emergency notifications, and status updates. Using multiple communication channels also reduces reliance on any single method during a disruptive event.
Targeted Alerting and Automated Escalation
Not every critical event requires notifying everyone.
Many incidents require a specific person or team to act. Modern CEM processes can use schedules, responsibilities, or escalation rules to determine who should receive an alert.
If the first responder does not acknowledge it, the incident can automatically escalate until someone takes ownership.
Incident Management and Response Coordination
Critical events often cross departmental boundaries.
Incident management and collaboration capabilities help teams maintain a shared view of the event, coordinate actions, document decisions, and track progress toward resolution.
Response Plans, Automation, and Analytics
Predefined response plans reduce the number of decisions that need to be made during a crisis. Workflows can trigger notifications, mobilize response teams, create incident records, or initiate remediation processes.
Analytics then provide insight into notification delivery, acknowledgment, escalation, response times, and resolution – helping teams improve future crisis response.
Where SIGNL4 Fits Into Critical Event Management
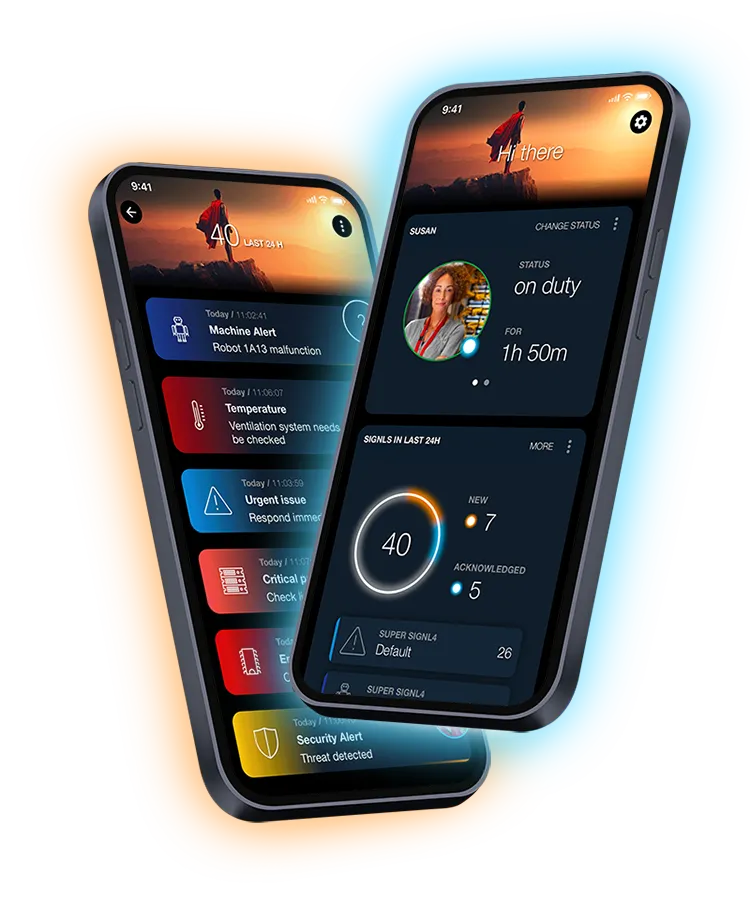
SIGNL4 focuses on a specific part of critical event management: turning detected critical events into reliable human response.
Monitoring, security, IoT, ITSM, and other systems are often very good at detecting when something is wrong. When an event requires human intervention, however, someone still needs to know about it and take action.
SIGNL4 adds mobile push, SMS, and voice alerting, on-call scheduling, automated escalation, acknowledgments, mobile incident collaboration, stakeholder communication, and response analytics.
Rather than replacing monitoring, risk intelligence, mass notification, or incident management software, SIGNL4 can connect events from existing systems with the people responsible for responding. Learn more about SIGNL4’s features!
Your systems detect. The right people respond.
Frequently Asked Questions
What is critical event management?
Critical event management is the process of identifying, assessing, communicating, and responding to disruptive events that can affect people, facilities, technology, operations, or business continuity.
What is a critical event management platform?
A critical event management platform is software that supports organizations in managing critical events. Depending on the platform, this may include threat monitoring, risk intelligence, situational awareness, mass notification, emergency communications, incident management, incident response, automation, and analytics.
What is the difference between CEM and mass notification?
Mass notification focuses primarily on reaching groups of people quickly. Critical event management has a broader scope and can also include threat intelligence, situational awareness, crisis management, incident response, response coordination, and analytics.
How does CEM support operational resilience?
CEM supports operational resilience by helping organizations identify disruptions, communicate relevant information, mobilize responders, coordinate action, and restore normal operations. Incident analysis can also help improve future response plans.
Can CEM software integrate with existing systems?
Yes. Modern CEM platforms commonly use APIs, webhooks, and pre-built integrations to connect with monitoring, security, ITSM, IoT, HR, collaboration, and other operational systems.
From Critical Event to Coordinated Response
Critical event management is ultimately about connecting information with action.
Risk intelligence can identify potential threats. Situational awareness helps teams understand what is happening. Mass notification and emergency communications keep people informed. Incident management helps coordinate the work.
But when a critical event requires human intervention, someone still has to respond.
That connection between detection, communication, and response should be a central consideration when evaluating critical event management platforms.
Start with the critical events that matter most to your organization. Understand how they are detected, how information flows, who needs to act, and where delays can occur. Then choose the CEM capabilities – and combination of technologies – that make the entire process faster, clearer, and more reliable.
